Guide
Every link, blocked.
Veyramesh blocks every member link by default. Why we chose that, what it costs on day one, and how staff and trusted users still share links safely.
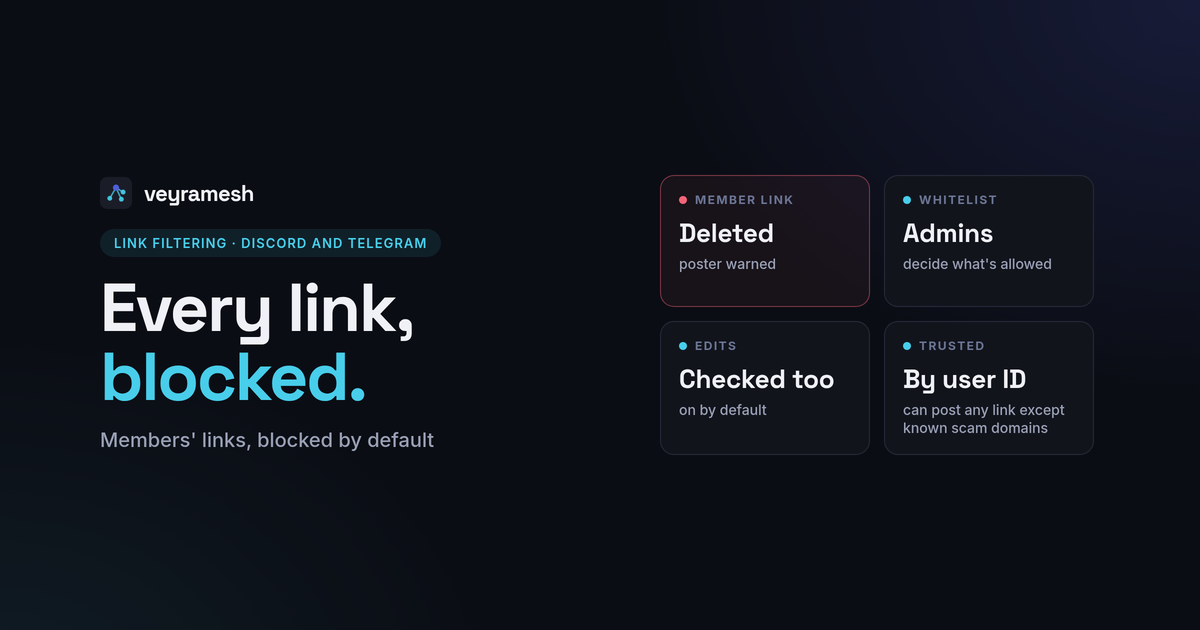
That's the Veyramesh default I'd defend first.
Post a link as a member in a Discord server or Telegram group running Veyramesh and, unless an admin has whitelisted the domain, the message is deleted and you get a warning. Keep doing it and the community's own rules kick in: a timeout, a kick or a ban, whichever they picked.
Staff and trusted users can post any link except known scam domains, which are still removed and flagged as a possible hijacked account.
On Telegram, that check only matches confirmed known scam domains.
Link filtering is always on.
Why start there
Years in web3 taught me one thing. Mod teams can't delete scams as fast as scammers post them, on Discord or Telegram.
Back at Neon EVM we got hit with over 1,000 scam messages in an hour. We installed a bot mid-attack to delete every link. It felt like a war.
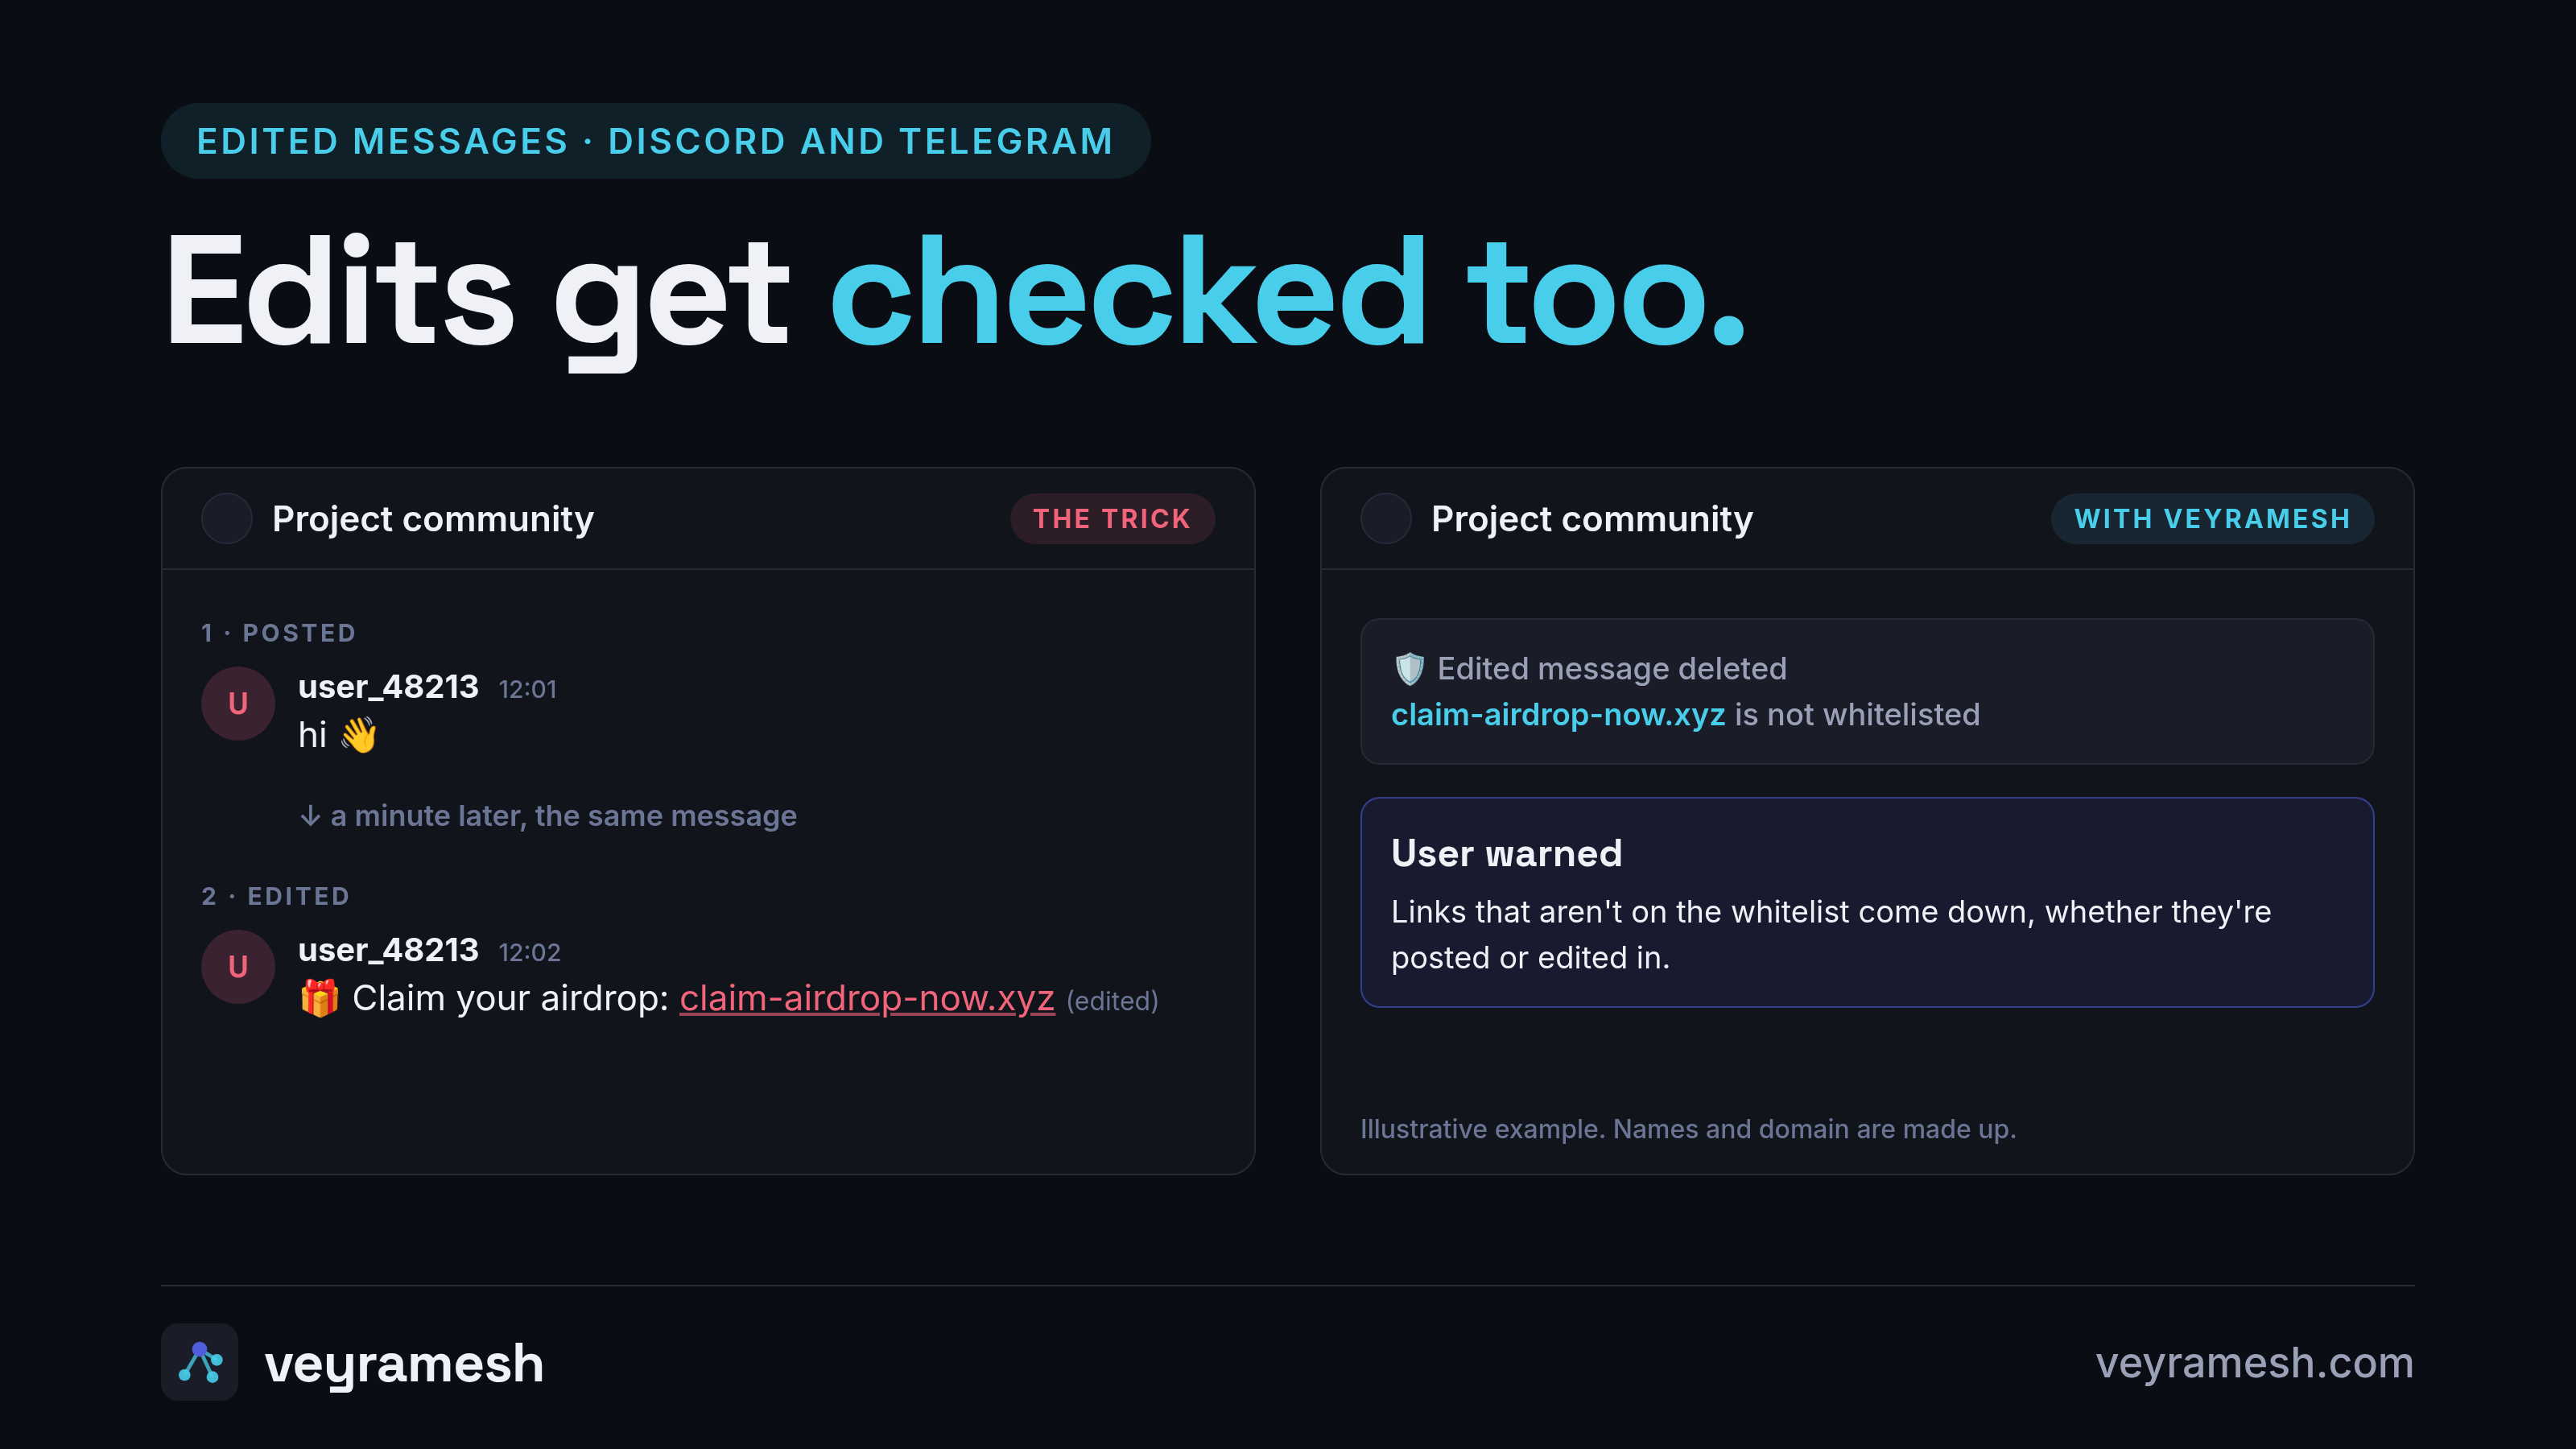
Even then some got through. Mainly when a scammer posted "hi", waited, then edited the message into a scam URL.
That's why Veyramesh checks edited messages too, by default, on both Discord and Telegram.
Most of the scams worth worrying about in a community chat need someone to click something. A fake claim page. A fake support desk. A lookalike domain. An invite to somewhere else.
So the question I kept coming back to was this. Which links does this community actually need?
For most, it's a short list. The website. The docs. X. Maybe GitHub.
Everything else can wait until someone with admin rights says yes.
I wanted the default to do the boring job, so mods aren't deleting links by hand at silly o'clock while a scam sits in the chat.
The annoying bit
Honest version: block-all is annoying at first.
Day one, a member posts the docs link and it vanishes. Someone shares the project's X account and gets a warning.
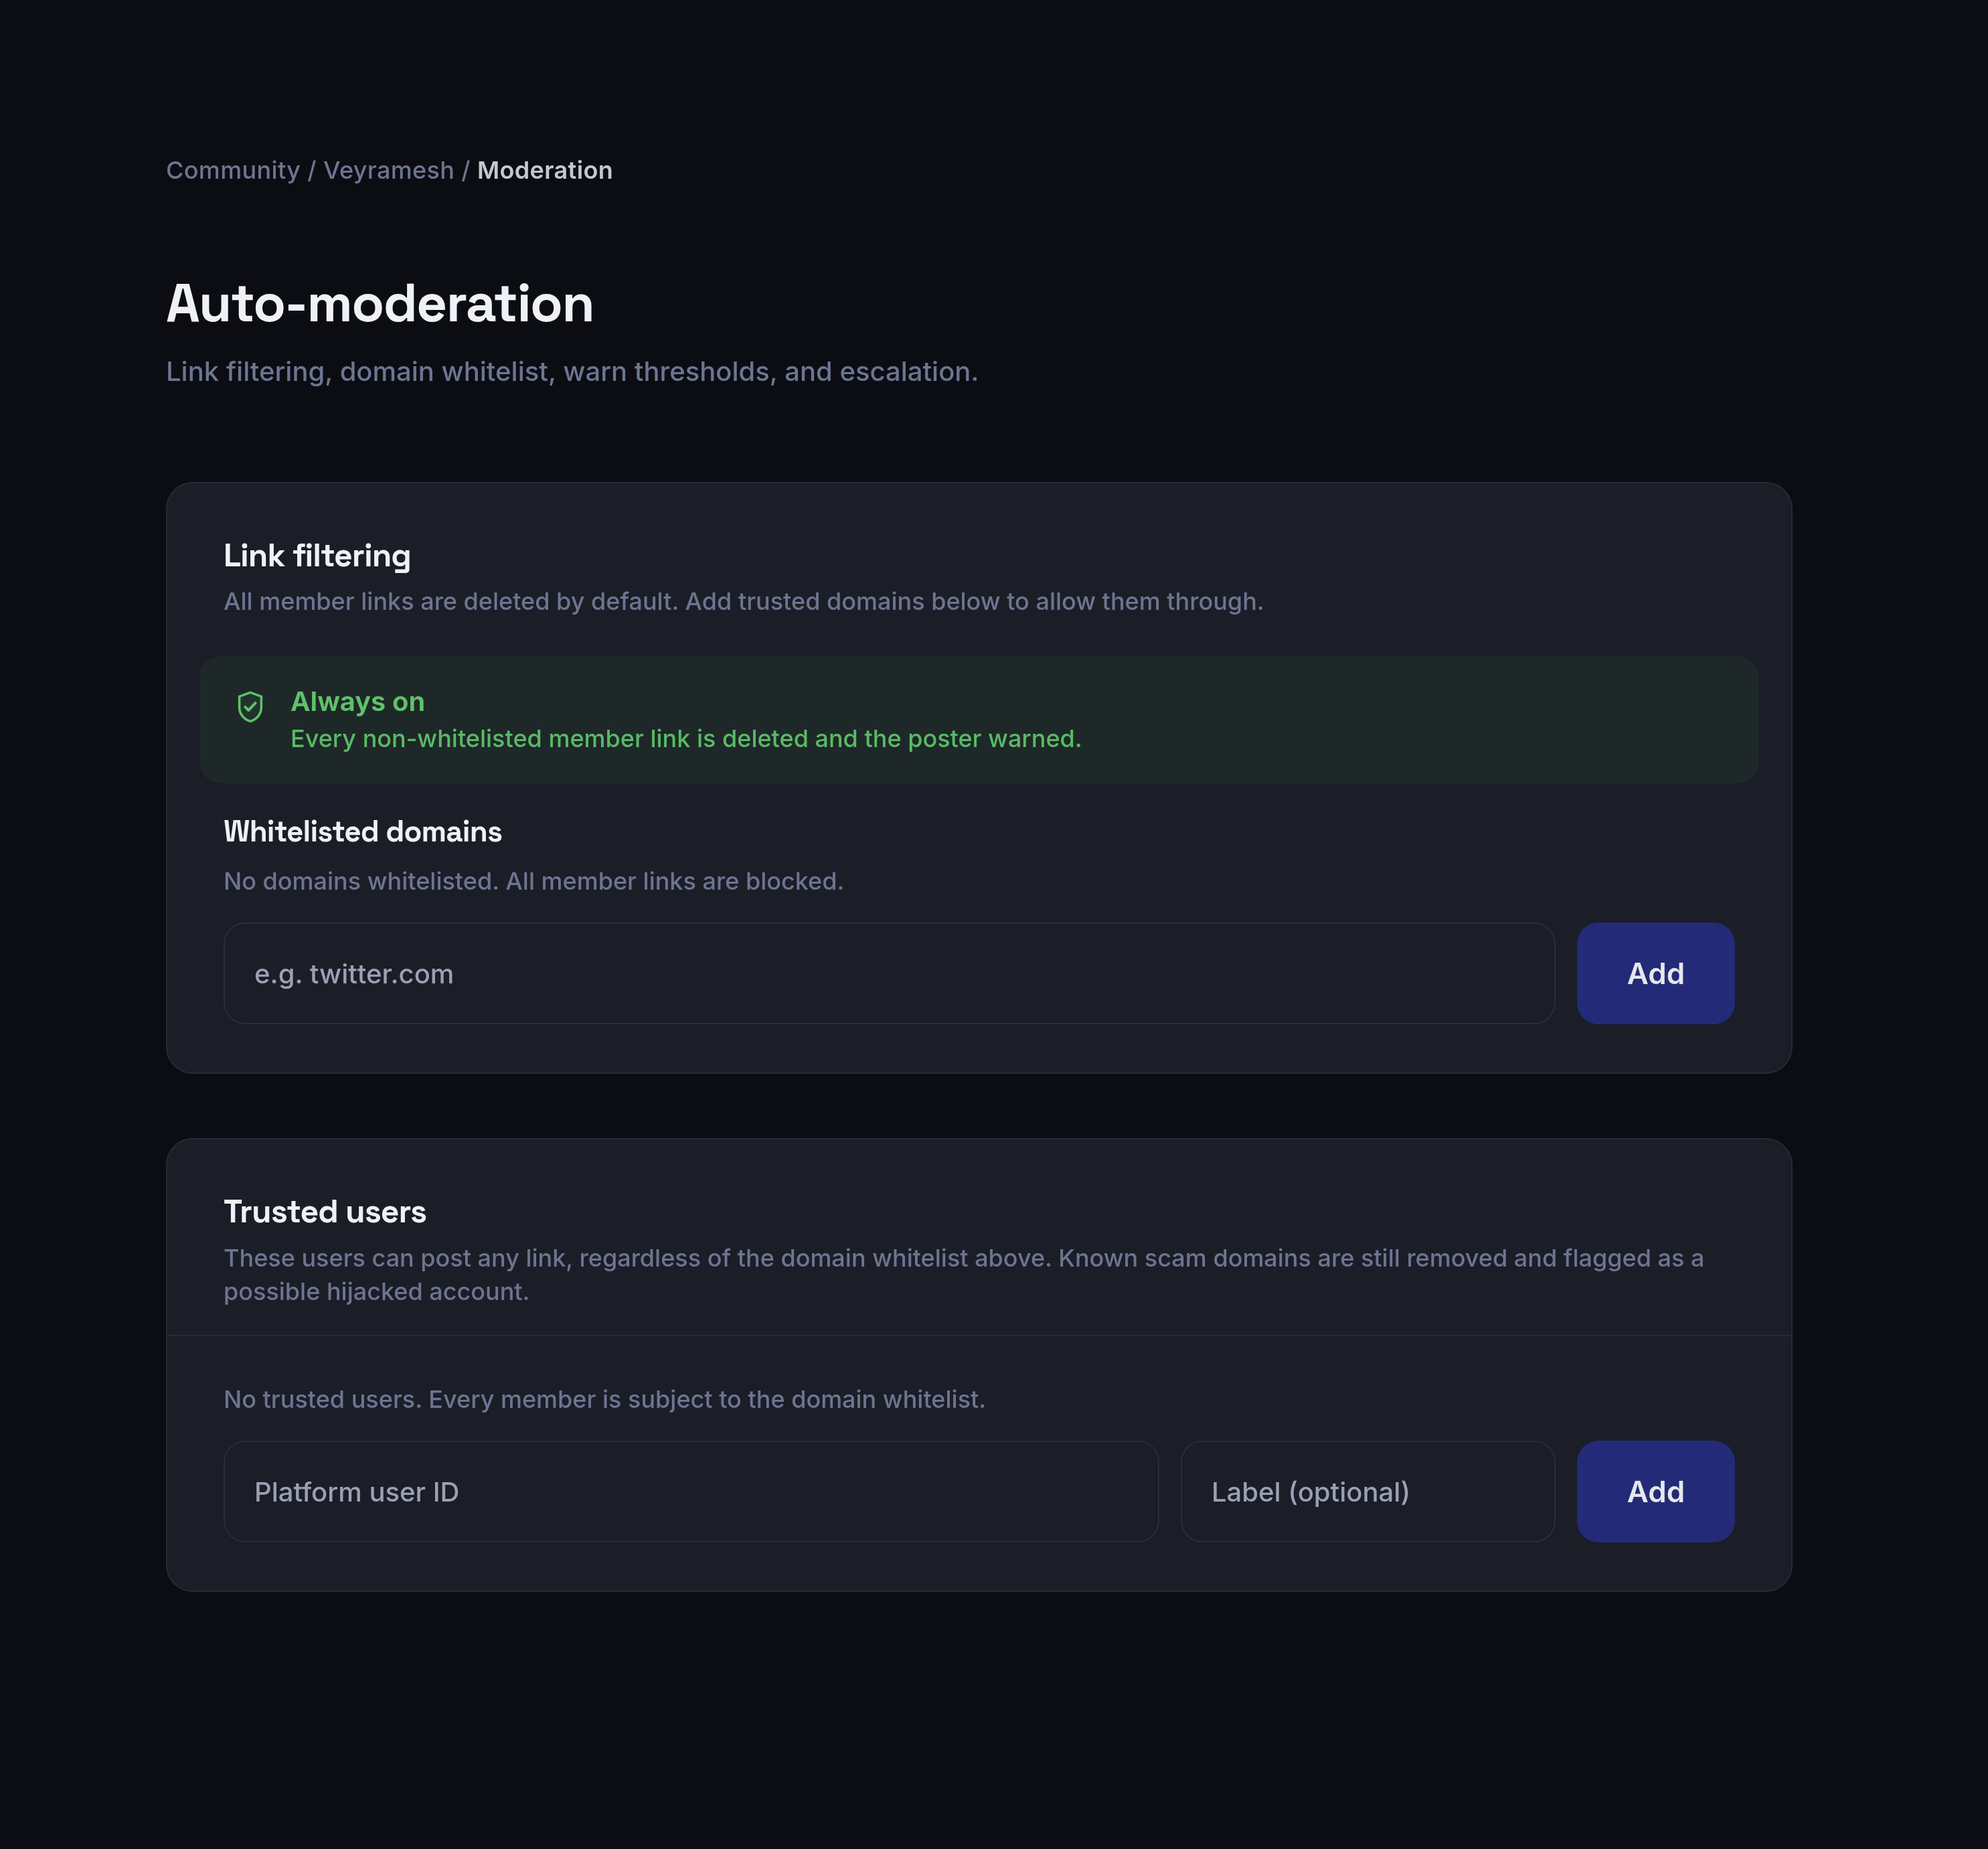
The fix is boring. Whitelist before launch week. List the domains your community genuinely uses, add them, then open the doors.
For people who need to share anything, there are Trusted users. Whoever posts the weekly round-up, or anyone without mod rights who needs to share links. They're added by platform user ID and can post any link except known scam domains, which are still removed and flagged as a possible hijacked account.
Keep that list short. Every name on it is an account you're trusting with any link except known scam domains, and accounts get compromised too.
A whitelist isn't a blank cheque
Whitelisting a domain doesn't wave everything on it through.
Discord login-style links, like authorise and QR-login pages, stay blocked even though discord.com is fine. And drainer-style paths on shared hosts like GitHub, Notion, Google Docs and Medium still get checked.
Scammers love a trusted domain. So the filter keeps looking.
Discord and Telegram
The two platforms don't behave the same, so here's which does what.
On Discord, a first-offence high-risk or phishing link gets a 1-hour timeout on top of the delete.
On Telegram, if moderation settings are on, a new join can raise a security alert. It never auto-bans.
Raid panic mode is off until you switch it on. When a lot of accounts pile in at once you get a "Raid detected" alert. On Discord it times members out. On Telegram, new joiners in the wave can't verify until it ends, and any who already had are muted again.
Raid panic mode doesn't remove anyone. The point is buying admins time to look.
Bots are part of the attack surface
In October, Double Counter, a verification bot used in a lot of Discord servers, published a detailed incident report: https://doublecounter.gg/blog/security-incident-october-2026
According to their report, an attacker got into its infrastructure, took the bot's Discord token and used it to post links to their own Discord server in about 50 large servers. The messages appeared as sent by Double Counter.
I'm not here to pick at anyone. That could happen to any bot team, and the write-up is worth reading in full.
And to be straight about it: link filtering wouldn't have stopped that one. It covers people, not other bots, so a hijacked bot's posts go straight past it.
Bot permissions are the separate defence. Give every bot the least it needs to do its job, ours included, and check which ones can post at all.
Where it's at
I'd rather explain a deleted docs link on day one than a drained wallet on day thirty.
Link filtering is part of the free Veyramesh bot, and it stays free after launch. Here is how to set it up.
Everything is free until 31 December. On 1 January, communities already on Veyramesh get a 14-day Pro trial automatically.
If you run a Discord or Telegram community, whitelist first and open the doors second.
Add Veyramesh to your community and set up your whitelist before launch week.